About Me
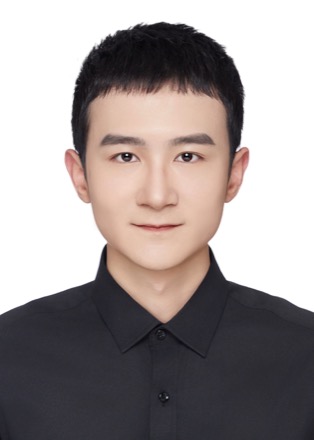
Hi! My name is Wenzhe Yi (易文哲), I’m currently a Ph.D. student at the School of Cyber Science and Engineering, Wuhan University, supervised by Prof. Juan Wang. Before that, I obtained my Bachelor’s degree from Wuhan University.
Since September 13, 2026, I have also been a visiting Ph.D. student at Nanyang Technological University (NTU), supervised by Asst. Prof. Wei Dong and Prof. Xiaofeng Wang. My visit is supported by the China Scholarship Council (CSC).
Research Interests
My research focuses on privacy and security in machine learning, particularly data reconstruction and model inversion attacks and defenses. I study how to protect sensitive data in collaborative learning and inference, including through confidential computing. My current interests also include privacy and security in large language models and text-to-image models.
Selected Publications
Palladium: Guarding Neural Network Training with Confidential Computing
Wenzhe Yi†, Mengda Yang†, Juan Wang*, Hongxin Hu, Ziang Li, Xiaoyang Xu
IEEE TDSC, 2026
Protecting neural network training through confidential computing.
Paper
Learning to Defend: Auto-Augmentation Search Against Model Inversion Attacks
Wenzhe Yi, Xiaoyang Xu*, Yong Zhuang*, Juan Wang*, Ziang Li, Hongxin Hu
IEEE TIFS, 2026
Searching for data augmentations to defend against model inversion attacks.
Paper
Membership inference attacks against split inference via knowledge transfer
Wenzhe Yi†, Mengda Yang†, Juan Wang*, Hongxin Hu, Ziang Li, Xiaoyang Xu, Yu He, Yao Wang
Neurocomputing, 2026
Investigating membership privacy in split inference through knowledge transfer.
Paper
† Equal contribution; * Corresponding author. All publications.
News
[9/2026] I started my visit to Nanyang Technological University (NTU) on September 13, supervised by Asst. Prof. Wei Dong and Prof. Xiaofeng Wang, with support from the China Scholarship Council (CSC)!
[5/2026] I have been awarded the scholarship by China Scholarship Council (CSC) to study as a visiting Ph.D. student at Nanyang Technological University (NTU) for 12 months!
[5/2026] One paper titled “Learning to Defend: Auto-Augmentation Search Against Model Inversion Attacks” got accepted in IEEE TIFS!
[1/2026] One paper titled “GEIA: Generative Enhancement Inversion Attack Targeting Machine Unlearning” got accepted in ICASSP 2026!
[1/2026] One paper titled “Can Data Augmentation Become a Privacy Shield for Model Inversion Attacks?” got accepted in ICASSP 2026!
Earlier news
- [1/2026] One paper titled “SLeak: Multi-Target Privacy Stealing Attack against Split Learning” got accepted in IEEE TPAMI!
- [11/2025] One paper titled “Membership inference attacks against split inference via knowledge transfer” got accepted in Neurocomputing!
- [8/2025] One paper titled “HVGuard: Utilizing Multimodal Large Language Models for Hateful Video Detection” got accepted as main in EMNLP 2025!
- [5/2025] One paper titled “Stealing Data from Active Party in Vertical Split Learning” got accepted in ECML-PKDD 2025!
- [3/2025] One paper titled “BiFD: A Bidirectional Feature Discrepancy Defense against Hijacking Attack in Split Learning” got accepted in ICME 2025!
- [2/2025] One paper titled “From Head to Tail: Efficient Black-box Model Inversion Attack via Long-tailed Learning” got accepted in CVPR 2025!
- [11/2024] One paper titled “I know what you MEME! Understanding and Detecting Harmful Memes with Multimodal Large Language Models” got accepted in NDSS 2025!
- [2/2024] One paper titled “Penetralium: Privacy-Preserving and Memory-Efficient Neural Network Inference at the Edge” got accepted in FGCS!
- [2/2024] One paper titled “A Stealthy Wrongdoer: Feature-Oriented Reconstruction Attack against Split Learning” got accepted in CVPR 2024!
- [9/2023] One paper titled “GAN You See Me? Enhanced Data Reconstruction Attacks against Split Inference” got accepted in NeurIPS 2023!
- [8/2023] One paper titled “Enhance the trust between IoT devices, mobile apps, and the cloud based on blockchain” got accepted in JNCA!
- [9/2022] One paper titled “Measuring Data Reconstruction Defenses in Collaborative Inference Systems” got accepted in NeurIPS 2022!
Publications
†: equal contribution; *: corresponding author
2026
Palladium: Guarding Neural Network Training with Confidential Computing
Wenzhe Yi†, Mengda Yang†, Juan Wang*, Hongxin Hu, Ziang Li, Xiaoyang Xu
IEEE Transactions on Dependable and Secure Computing (IEEE TDSC)
Learning to Defend: Auto-Augmentation Search Against Model Inversion Attacks
Wenzhe Yi, Xiaoyang Xu*, Yong Zhuang*, Juan Wang*, Ziang Li, Hongxin Hu
IEEE Transactions on Information Forensics and Security (IEEE TIFS)
GEIA: Generative Enhancement Inversion Attack Targeting Machine Unlearning
Yaoxuan Ma, Xiaoyang Xu*, Juan Wang*, Wenzhe Yi, Yaxin Liu
IEEE International Conference on Acoustics, Speech, and Signal Processing (ICASSP), 2026
Can Data Augmentation Become a Privacy Shield for Model Inversion Attacks?
Wenzhe Yi, Xiaoyang Xu, Yong Zhuang, Juan Wang*
IEEE International Conference on Acoustics, Speech, and Signal Processing (ICASSP), 2026
SLeak: Multi-Target Privacy Stealing Attack against Split Learning
Xiaoyang Xu, Wenzhe Yi, Juan Wang*, Hongxin Hu, Mengda Yang, Ziang Li, Yong Zhuang, Yaxin Liu, Mang Ye
IEEE Transactions on Pattern Analysis and Machine Intelligence (IEEE TPAMI)
Membership inference attacks against split inference via knowledge transfer
Wenzhe Yi†, Mengda Yang†, Juan Wang*, Hongxin Hu, Ziang Li, Xiaoyang Xu, Yu He, Yao Wang
Neurocomputing
2025
HVGuard: Utilizing Multimodal Large Language Models for Hateful Video Detection
Yiheng Jing†, Mingming Zhang†, Yong Zhuang*, Jiacheng Guo, Juan Wang*, Xiaoyang Xu, Wenzhe Yi, Keyan Guo, Hongxin Hu
Proceedings of the 2025 Conference on Empirical Methods in Natural Language Processing (EMNLP main), 2025
Stealing Data from Active Party in Vertical Split Learning
Yaxin Liu, Xiaoyang Xu, Wenzhe Yi, Yong Zhuang, Juan Wang*, Mengda Yang, Ziang Li
European Conference on Machine Learning and Principles and Practice of Knowledge Discovery in Databases (ECML-PKDD), 2025
BiFD: A Bidirectional Feature Discrepancy Defense against Hijacking Attack in Split Learning
Xiaoyang Xu, Wenzhe Yi, Juan Wang*, Yong Zhuang, Mengda Yang, Ziang Li, Yaxin Liu
IEEE International Conference on Multimedia & Expo (ICME), 2025
From Head to Tail: Efficient Black-box Model Inversion Attack via Long-tailed Learning
Ziang Li, Hongguang Zhang, Juan Wang*, Meihui Chen, Hongxin Hu, Wenzhe Yi, Xiaoyang Xu, Mengda Yang, Chenjun Ma
IEEE/CVF Conference on Computer Vision and Pattern Recognition (CVPR), 2025
I know what you MEME! Understanding and Detecting Harmful Memes with Multimodal Large Language Models
Yong Zhuang†, Keyan Guo†, Juan Wang*, Yiheng Jing, Xiaoyang Xu, Wenzhe Yi, Mengda Yang, Bo Zhao, Hongxin Hu
The Network and Distributed System Security Symposium (NDSS), 2025
2024
Penetralium: Privacy-Preserving and Memory-Efficient Neural Network Inference at the Edge
Mengda Yang, Wenzhe Yi, Juan Wang*, Hongxin Hu, Xiaoyang Xu, Ziang Li
Future Generation Computer Systems (FGCS)
A Stealthy Wrongdoer: Feature-Oriented Reconstruction Attack against Split Learning
Xiaoyang Xu, Mengda Yang, Wenzhe Yi, Ziang Li, Juan Wang*, Hongxin Hu, Yong Zhuang, Yaxin Liu
IEEE/CVF Conference on Computer Vision and Pattern Recognition (CVPR), 2024
2023
GAN You See Me? Enhanced Data Reconstruction Attacks against Split Inference
Ziang Li, Mengda Yang, Yaxin Liu, Juan Wang*, Hongxin Hu, Wenzhe Yi, Xiaoyang Xu
Advances in Neural Information Processing Systems (NeurIPS), 2023
Enhance the trust between IoT devices, mobile apps, and the cloud based on blockchain
Juan Wang*, Wenzhe Yi, Mengda Yang, Jiaci Ma, Shengzhi Zhang, Shirong Hao
Journal of Network and Computer Applications (JNCA)
2022
Education
[2026.09.13 – present] Visiting Ph.D. student, Nanyang Technological University (NTU). Supervised by Asst. Prof. Wei Dong and Prof. Xiaofeng Wang. Supported by the China Scholarship Council (CSC).
[2024.09 – present] Ph.D. in Cyberspace Security, Wuhan University. Supervised by Prof. Juan Wang.
[2022.09 – 2024.06] Master’s studies in Cyberspace Security, Wuhan University. Supervised by Prof. Juan Wang. (Part of the 1+4 Program)
[2018.09 – 2022.06] Bachelor’s degree in Information Security, Wuhan University.
Academic Service
Conference Reviewer / Program Committee Member:
- AAAI 2027, ICLR 2027
- CVPR 2026, ICLR 2026, AAAI 2026
- NeurIPS 2025, ICCV 2025, ECML-PKDD 2025, ICME 2025
Awards
- Lei Jun Graduate Student Scholarship in Computer Science, Wuhan University, 2025.
- Huawei Scholarship, Wuhan University, 2024.
- Wuhan University Outstanding Academic Scholarship (First Prize), 2023.
- Wuhan University Outstanding Graduate Student Award, 2023.
- The 1st Privacy Computing and Data Security Challenge, Second Prize, 2022.
- Wuhan University Outstanding Student Award, 2021.
- Wuhan University Outstanding Student Scholarship (Third Prize), 2021.